From Insight to Autonomous Action​

Q4 / 2026 Product Releases

Why is this release important?

Turn trusted data into AI-guided remediation with governed access, ​prioritized fixes, and expanded patching.​

Connected AI-powered experiences and MCP access across the Ivanti Neurons platform

Expand AI across the Ivanti Neurons platform through native AI capabilities and MCP-enabled access to trusted operational data. Together, these experiences enable natural-language interaction, guided workflows, and more informed action — from AI-assisted query building and scripting to insights, recommendations, and conversational reporting, helping teams troubleshoot more effectively and gain a deeper understanding of their IT environments.

Day Zero Support for the Newest Operating Systems

Be ready as users upgrade their devices or purchase new gear. With Day Zero support for macOS 27, iOS 27, and Android 17 — including Apple Declarative Device Management inside the same platform managing traditional endpoints — IT and security teams can detect, manage, and secure new tech from the very first day, ensuring device inventory stays grounded in truth.

Woman wearing glasses in front of several monitors displaying code and data

Ivanti Neurons Platform

Ivanti Neurons Platform expands AI capabilities through MCP Server Access, and strengthens native tools with the introduction of tools such as Insights & Recommendations and AI Reporting. The release helps teams access relevant information, prioritize and make informed decisions.

Learn More

GA — MCP (Model Context Protocol) Server access

Expands customer access to MCP through admin-controlled activation. Grounded in the Ivanti Neurons System of Record, MCP provides a governed connection between AI experiences and trusted operational information across the platform, enabling more contextual, relevant, and actionable AI interactions. Customers entitled to the Ivanti Neurons Platform can now enable read-only MCP Server access to begin securely exploring trusted operational data with AI and see MCP Server in action.

Tech Preview — AI Insights & Recommendations

AI Insights & Recommendations uses trusted operational data from the Ivanti Neurons System of Record to surface prioritized issues and recommended next steps across devices, vulnerabilities, the software estate, and other operational areas. The initial experience helps administrators focus on what matters most but does not automatically execute recommended actions.

AI Insights & Reccomendations: Prioritize IT and Security Rsks with AI Insights and Recommendations

Tech Preview — Conversational AI Reporting (Tier 2)

Create reports through natural-language interactions and generate reporting outputs directly through a conversational experience. Powered by trusted operational data from the Ivanti Neurons Platform System of Record, Conversational AI Reporting reduces manual report creation and simplifies access to operational insights.

AI Reporting: Turn IT and Security Data Into Actionable AI Reporting

Autonomous Endpoint Management

Automated sharing of exposure information ignites remediation workflows, while security and IT teams get more granular control over patch configurations. Plus, organizations are equipped to enroll, deploy and support the latest devices and operating systems.

Learn More

Autonomous Patch Management

Get straight to what matters most—AI-generated insights surface your top three patch deployment statuses, prioritized by impact, so you can act fast instead of digging through dense data (currently in tech preview).

Digital Experience Management

  • Improved governance of Bot ownership and and secure collaboration among shared Bots
  • Enhanced variable outputs for orchestration, APIs enables more sophisticated automation and cleaner integrations
  • AI JavaScripts enable increased reusability, accelerate developments, and improve automation consistency

Predictive Remediation

A tighter remediation loop with stage-then-activate control in Patch Groups, plus ownership-aware visibility and sharing. Smarter, lower-effort prioritization as business criticality auto-imports from three more scanners, normalized to 1–5 with a Medium default. And a more enterprise-ready platform: scope-aware access control, honest scope messaging, sortable grids, and architecture built to scale.

Unified Endpoint Management

  • Linux support delivers on customer requested expansion of platform coverage, and supports patch management initiatives
  • Foundational work on End User Workspace lays groundwork for delivering new workspace capabilities through a unified experience
  • Enhancements for security, governance and enterprise readiness: Enables administrative delegation, supports supports security and enterprise governance requirements, and assists customers migrating from on-premises environments
  • Updates to auditing capabilities for improved compliance, traceability, and operational governance
  • Apple Warranty connector increases visibility into hardware lifecycle and warranty status
  • Chip-to-Cloud bulk enrollment significantly reduces deployment effort and improves adoption of remote management capabilities
  • Non-Persistent VDI support improves management of virtual desktop environments, keeps reporting accurate, and provides a stronger migration path from on-premises solutions

Mobile Device Management

Administration/Platform:

  • Wipe/Retire Protection – approval before device wipe/retire
  • Restricting device registration by OS platform
  • Audit logs for device enroll/unenroll within a Space
  • Device OS type as a filter criteria in Device Cleanup Settings.
  • Phased rollout of Android in-house apps, allowing more control over deployment to a large number of devices.
  • Improved tracking and reporting of DDM app management status across devices

Apple:

  • Apple OS 27 ongoing rollout of features
  • Lockdown Mode status enables fleetwide reporting on device lockdowns
  • Enhanced logging feature speeding device logs export to Apple Care
  • iOS/macOS 27 admin control over Safari privacy defaults across device fleet
  • MacOS app control to prevent unauthorized applications running on your macOS fleet
  • New Safari minimum version check for BYOD device enrollment

Android:

  • Simplify device provisioning with support for self-signed certificates in Ivanti Go
  • Protect sensitive information with notification redaction on locked devices' screen
  • Avoid user disruption with safe updates for in-house applications
  • Gain visibility into eSIM management status to enforce carrier policies
  • Accelerate shared kiosk sign-in with alternate username for LDAP Users
  • Maintain uninterrupted kiosk experiences during configuration changes
  • Strengthen security with automatic device lock outside trusted networks
  • Reduce downtime with battery health insights for Unitech devices

Application Control & Privilege Management

Scope-based app controls improves administrative security, governance, and alignment with enterprise access controls, including:

  • Cloud asset information
  • Additional device ownership, lifecycle, and classification data
  • Expanded support relationship context
  • Improved onboarding through global tenant orchestration
  • Insight & Recommendations
  • AI Reporting Agent
  • Patch Insights
  • AI Diagnostics Agent

Endpoint Manager

  • Support for Ubuntu 26
  • Windows 11 26H2 support

Endpoint Manager Mobile (EPMM)

Administration/Platform:

  • VPP v2 support

Apple:

  • Visibility to device component health for iOS/iPadOS 27
  • New device details reported status for iOS/macOS 27

Android:

  • Tunnel VPN integration into Mobile@Work client

Advanced Mobility Capabilities

Secure Productivity Apps

Email+ for Android: Font type selection gives users more control when composing emails. External sender highlighting helps users identify messages originating outside their organization. Android 17 support and bug fixes

Email+ for iOS: Apple platform compatibility updates, including iOS 27 support; Persistent token support to reduce re-enrollment prompts; and a New administrator configuration option for Secure HTML Mode.

Sentry

  • Security enhancements
  • TLS 1.3 support
  • Migration to Oracle Linux 9.7
  • Support for Microsoft Hyper-V 2025

Access

  • Support for One Ivanti login across MDM and Neurons platform
  • Microsoft Entra External Authentication Methods support to provide customers conditional access for Entra ID within the Ivanti platform.

Patch Content Catalog

New products and major versions are added to the patch content catalog regularly and your input helps shape what's next. Submit and vote on priorities in Aha! to guide our roadmap.

Risk-based Vulnerability Management (RBVM)/Application Security Posture Management (ASPM)

We've strengthened risk data with CVE-level findings from Cortex Xpanse and richer CMDB context from ITSM, so you get fewer false signals and more accurate prioritization. Analysts spend less time on repetitive configuration thanks to bulk column and group selection in Playbook. And SLA management gets sharper with visibility into newly-overdue findings, not just the ones already 30+ days late, so you can catch problems before they escalate.

Man wearing glasses and a headset smiles at a computer workstation

IT Service Management

Packaging

New packaging for Ivanti’s ITSM product and solution family supports your critical journey from core service and asset management to full enterprise service management as well as your evolution from manual service management operations to agentic AI-driven workflows and fully autonomous operations. The previous packaging structure that included standalone products, various bundling options, and solution packages, is now streamlined into two solutions delivered on the Ivanti Neurons Platform:

  • Ivanti ITSM — Delivers all core IT service and asset management capabilities, plus AI Analyst Assist for ITSM, Asset Discovery, and Discovery from the Ivanti Neurons Platform.
  • Ivanti ITSM Premium — Extends the portfolio with intelligent automation, Agentic AI for self-service, and support for a range of Enterprise Service Management workflows, including HR, Facilities, and others.

These solutions interoperate flawlessly with Ivanti’s Autonomous Endpoint Management solution, providing a clear path to intelligent, autonomous operations built on authoritative data.

Agentic AI

This release brings the AI Self-Service Agent to general availability, making Agentic AI in ITSM easier to access, more governed, and more measurable.

Key capabilities:

  • WebChat access — Eligible self-service users can interact with Agentic AI through a web-based chat interface in Ivanti ITSM, without requiring Microsoft Teams. The interface supports live agent transfer.
  • Governed incident template selection — The Incident creation agent matches only templates configured under SelfService Templates, giving administrators a controlled template pool for AI-assisted incident creation.
  • Richer incident context with AI attribution — For AI-created incidents, the template description is preserved, a timestamped AI-generated conversation summary is appended and the Source is consistently set to Agentic AI.
  • Clearer service request next steps — After a service request form is selected, users can confirm they're all set, start a new query or transfer to a live agent.
  • Expanded service request analytics — New metrics track deeplinks opened, deeplink engagement rate and conversations with no deeplink opened.
  • Global outcome analytics — A new consolidated metric tracks incidents created plus service request forms opened through AI agent–provided deeplinks.
  • SharePoint as an external knowledge source for the Knowledge Base Agent — administrators can connect SharePoint sites to support AI-powered knowledge searches and responses.
  • Multilingual Agentic AI conversations — users can interact in their preferred supported language and receive responses in the same language.

Network Security

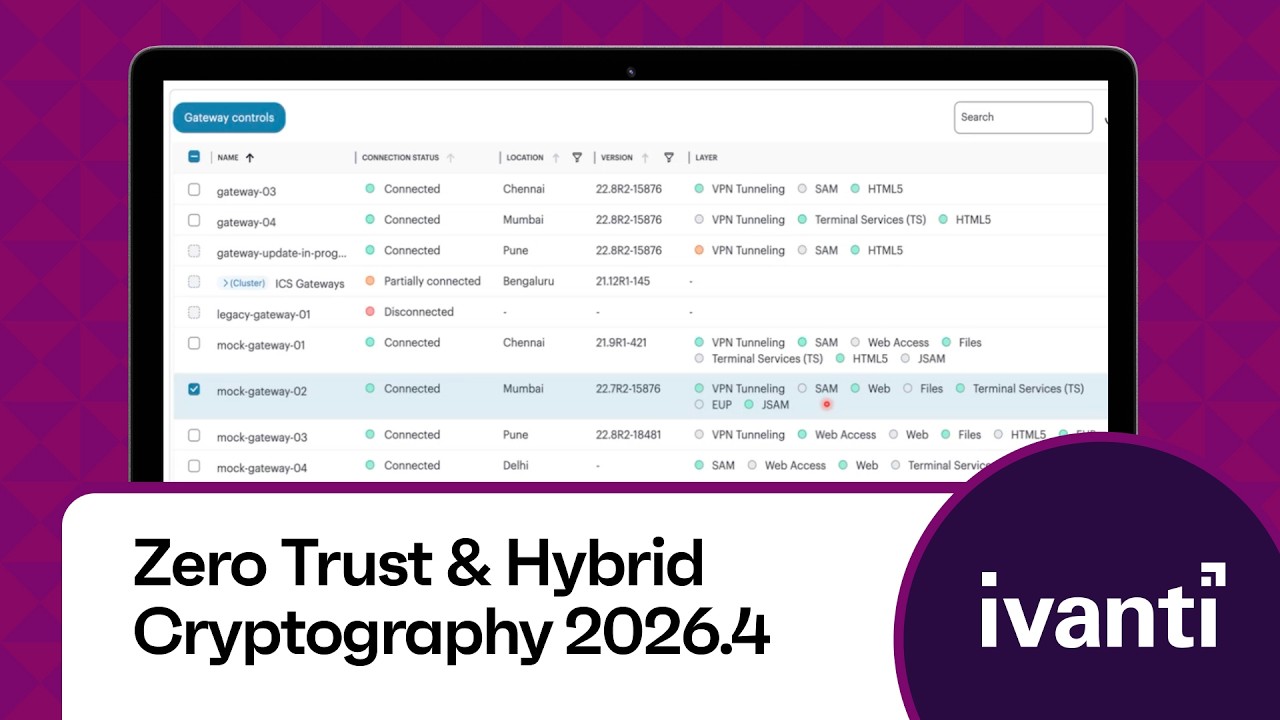
This quarter's updates strengthen Ivanti's network security portfolio through enhanced security resilience, simplified operations, expanded platform compatibility, greater deployment flexibility, and new threat monitoring capabilities across secure access, Zero Trust, cloud management, and network access control solutions. Investments in post-quantum cryptography readiness, platform modernization, policy and feature orchestration, multi-factor authentication, observability, and lifecycle management help organizations reduce operational overhead while improving security posture and service continuity. New capabilities across access, application delivery, endpoint, and cloud-based administration further support enterprise and managed service provider environments that require scalable, resilient, and future-ready infrastructure.

Learn More

Connect Secure

Ivanti Connect Secure (ICS) 25.1.4.0 advances secure access security, operational resilience, and platform modernization through post-quantum cryptography readiness, enhanced authentication and authorization controls, and expanded cloud-managed security capabilities. New support for large-scale OAuth group-based role mapping, RSA 8.8 migrations, authentication service fallback, TOTP reliability enhancements, extended HTTP/2 support for egress rewriter use cases, and secure-by-default browser protections strengthen security, performance, and availability. Extended cloud-managed controls delivered through Ivanti Neurons for Secure Access also enable organizations and managed service providers to more effectively manage features and services across deployments.

Release Notes

Ivanti Secure Access

Ivanti Secure Access expands centralized security operations with automated license monitoring, IOC-based threat detection through Integrity Monitor, WAF blacklist capabilities to detect or block threats, modular patching, OS-specific ISAC desktop packages, and selective toggling of L3, L4, and L7 features, including Web Access (Rewriter), Secure Application Manager (SAM), and Network-Level VPN Access. These capabilities help organizations and managed service providers reduce risk, respond more rapidly to emerging threats, simplify large-scale gateway operations, and maintain resilient, business-critical access services.

Release Notes

ZTA

Zero Trust Access expands deployment flexibility, scalability, and service continuity for modern Zero Trust environments. New capabilities include server-initiated connections, expanded resource access support, enhanced DNS gateway handling, and offline-access functionality designed to improve availability during controller outages. Together, these updates broaden customer deployment options while improving resiliency and user experience.

Release Notes

Secure Access Client

ISAC Desktop:

Ivanti Secure Access Client (ISAC) Desktop enhances endpoint access reliability, operating system readiness, and troubleshooting capabilities across Windows and macOS environments. Day Zero readiness for Windows 11 26H2 and macOS 27 enables customers to upgrade to new operating systems with confidence, while standardized ISAC 25.x versioning with ICS and IPS improves release consistency, interoperability, and lifecycle management. Post-quantum cryptography (PQC) readiness helps organizations prepare for future quantum-based threats, while fallback support for Windows Hello for Business, expanded proxy configuration capacity, and enhanced diagnostic tooling simplify deployment and administration. New Zero Trust Access capabilities including packet capture, simultaneous VPN and ZTA connectivity, DNS gateway enhancements, and offline-access support improve visibility, flexibility, and user experience.

Release Notes

ISAC Mobile:

Ivanti Secure Access Client (ISAC) Mobile delivers stronger mobile access security and platform readiness through expanded multi-factor authentication support, post-quantum cryptography enhancements, and operating system compatibility updates. Support for MFA with VPN On Demand and Per-App VPN strengthens authentication for mobile users, while PQC capabilities help safeguard sensitive communications against future cryptographic threats. Day Zero support for iOS 27 ensures ongoing platform compatibility, and new in-app feedback capabilities provide a streamlined channel for end-user input and continuous product improvement.

ISAC Mobile for iOS Release Notes 
ISAC Mobile for Android Release Notes

Application Delivery Controller (vADC)

Ivanti Application Delivery Controller (vADC) enhances security, certificate lifecycle management, and administrative efficiency across application delivery environments. New capabilities include FIPS support for Services Director, multi-site cluster API enhancements, centralized SSL certificate management, automated Let's Encrypt certificate renewal, and streamlined web application firewall rule updates. Together, these improvements simplify operations while helping organizations maintain secure, modern application delivery infrastructures.

Release Notes

Policy Secure

Policy Secure & Profiler network access control (NAC) extends support for the IPS 25.x software release to existing ISA6000 and ISA8000 hardware appliances, enabling customers to migrate from 22.x to 25.x and take advantage of updated security, functionality, and ongoing software support while planning their transition to new ISA appliances. This provides a more flexible modernization path that helps organizations streamline upgrades, extend the value of existing infrastructure, and maintain a consistent operational experience across their network access control environment.

Release Notes

Supply Chain

person interacting with a smart device in a warehouse.

Velocity Platform

  • The Velocity Console can now import a Velocity deployment file (.wldep) to help recover if a full Velocity Console Project is lost.
  • Enhanced screen rotation settings offer better control for device orientation.

Velocity Forms

  • Store-and-forward capabilities are now available for Forms! Forms can be downloaded to a device for completion even when a network connection isn’t available. Completed Forms can be transmitted once the device reconnects to the network and authenticates to the Ivanti cloud.
  • Duplicate an existing Form in the Forms Editor, and you're easily able to get started creating additional Forms for different processes. Say goodbye to creating common data fields over and over again for different Forms.