


Key Takeaways
- Protect the edge! The leadup to Patch Tuesday has several zero-days targeting network edge devices.
- Review asset and software lifecycles. A lot of end-of-support and end-of-life dates occurred in October and more will be occurring between now and January 2027.
- Microsoft Windows OS is the top priority this month to resolve the zero-day exploit (CVE-2026-96951).
What's happened since September Patch Tuesday
Here’s a fun fact to start this month. Ivanti’s Vulnerability Knowledge Base is now tracking more than 406,000 CVEs. Over 78,000 of them were disclosed in 2026 alone, which is more than the roughly 70,000 CVEs released in 2015 and earlier, going back to 1999.
- CVE Disclosure: 2026 year to date has already exceeded the full 2025 total by 64% (as of October 12). (Source: Ivanti Vulnerability KB)
- Exploitation: 2026 year to date has exceeded the full 2025 total by 33%. (Source: Ivanti Vulnerability KB)
- Patch Acceleration: 2026 year to date has reached 94% of the full 2025 total and is on pace to finish roughly 20% higher. (Source: Ivanti Patch Catalogue)
Edge devices and appliances dominated the weeks before this Patch Tuesday.
- Citrix disclosed a targeted NetScaler zero-day, CVE-2026-88779 (CVSS 8.7), that requires the appliance to be configured as a SAML service provider or identity provider.
- CISA flagged the critical FortiMail flaw CVE-2026-104286 (CVSS 9.8, unauthenticated file write) as actively exploited.
- SonicWall hotfixed CVE-2026-102255 (CVSS 10.0, pre-authentication SSRF in SMA1000) on October 6, and attack traffic appeared by October 9. Confirmed compromise isn’t established.
- On October 8, CISA added five older flaws to KEV (ProFTPD, ONLYOFFICE, Strapi, Struts, and BIND) following abuse by the China-linked Flax Typhoon.
- Ivanti disclosed a high severity unauthenticated bypass vulnerability (CVE-2026-104935) in Ivanti Connect Secure. Ivanti is aware of limited exploitation. Fixes are available for the 25.x and 22.x code lines, but Ivanti recommends moving to 25.x as soon as possible as the 22.x code lines will reach end of life on January 31, 2027.
Microsoft
Lifecycle is a key theme this month. Several products stopped receiving security updates this month:
- Office 2021 and Office LTSC 2021 reached end-of-support, along with Windows 10 2016 LTSB and IoT LTSB 2016.
- Windows 11 24H2 Home and Pro reached end of servicing, and Windows Server 2012/2012 R2 enter their final ESU year with no Year 4.
- Commercial Windows 10 ESU Year 1 ends October 13, with Year 2 running to October 12, 2027. Consumer ESU was extended to October 12, 2027.
- The final ESU phase for Exchange Server and Skype for Business Server expires October 31.
- Windows Server 2022 moves to extended support and needs no action.
Today's Microsoft release
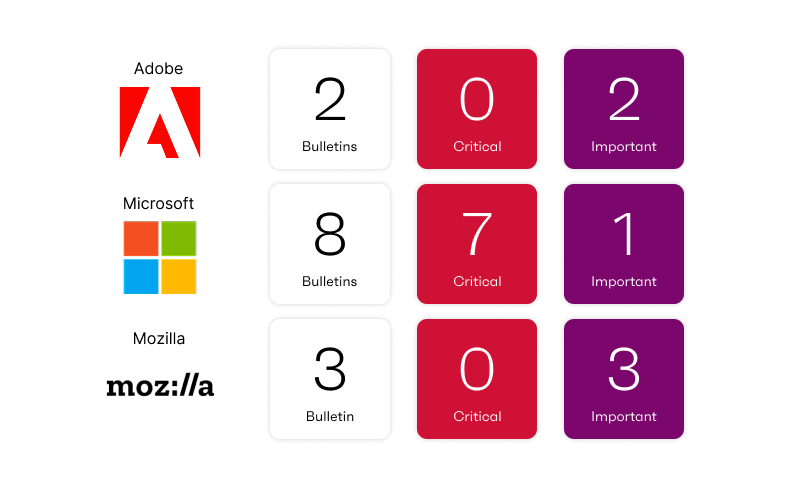
Microsoft fixed 1,407 CVEs this month, 78 rated Critical and 1,329 Important. That’s roughly 44% more than September’s record.
One vulnerability is confirmed exploited: CVE-2026-96951, a Windows Shell security feature bypass affecting Windows 10, Windows 11 and Windows Server 2012 R2 through 2025. Windows Shell has now been a zero-day target several times this year. Patch it first.
One vulnerability is publicly disclosed: CVE-2026-108398, a .NET Framework security feature bypass affecting .NET Framework 3.5 and 4.6.2 through 4.8.1. Public disclosure raises urgency because exploit code may follow.
Of the 78 Critical CVEs, 65 are remote code execution. Office accounts for 34 (19 in Excel), and several hit network-facing services: DHCP Server, Message Queuing, Remote Desktop Services, and QUIC. Exchange has a Critical RCE (CVE-2026-70571) for versions 2016 and 2019 whose ESU ends October 31.
Third-Party Update
Adobe
Adobe released 10 bulletins covering 141 CVEs, 15 of them Critical. Adobe is not aware of exploitation for any of them. Start with the two products holding every Critical:
- ColdFusion (APSB26-144): 10 Critical flaws, including three unauthenticated, network-reachable bugs rated 9.8 or higher (CVE-2026-105899, 10.0; CVE-2026-106622, 10.0; CVE-2026-106624, 9.8). Update to 2025.0.14 or 2023.0.26.
- Commerce (APSB26-153): five Critical flaws, including CVE-2026-103849 (10.0) and CVE-2026-92909 (9.8), both unauthenticated. Customers also need to apply the hotfix for CVE-2026-75650 from the September 7 APSB26-146 update.
The other eight bulletins are Priority 3: Photoshop (18 CVEs), Content Credentials SDK (30), Substance 3D Stager (16), FrameMaker (10), Substance 3D Designer (9), Dimension (7), Bridge (4) and Substance 3D Sampler (4).
Mozilla
Mozilla released Firefox 158, ESR 153.5 and ESR 115.43, fixing 79 unique CVEs, 30 rated high. Several allow sandbox escapes, including CVE-2026-109705, 109707, 109708, and 109712. Mozilla now issues one CVE per bug, which raises counts compared with earlier months. The advisories report no exploitation.
Ivanti October 2026 Security Update
Ivanti’s October security update addresses seven vulnerabilities across three products including Ivanti Patch for Intune and Ivanti Xtraction. Most notably, Ivanti disclosed CVE-2026-104935 (CVSS 8.6), an authentication bypass in Connect Secure that Ivanti says it is aware of limited exploitation of in the wild. Fixes are in 25.1.1.2, 25.1.3.0, 25.1.3.1 and 22.8R2.5, depending on the code line. A fix for a related privilege escalation flaw used in the same chain is due in the coming weeks.
October update to-do list
- Update the Windows OS to resolve the windows shell command injection zero-day exploit (CVE-2026-96951).
- Review the end-of-life list from Microsoft and ensure removal or mitigation of risk plans are in place.
- Execute your routine maintenance plan for the rest of the updates.